…NiRA warns against growing .ng domain names at expense of security
By Kingsley Samuel
The National Information Technology Development Agency, NITDA, has directed Ministries, Departments and Agencies, MDAs, to implement the Domain Name System Security Extensions, DNSSEC, and said compliance would form part of its cybersecurity assessment.
The agency said the measure was intended to reduce cyber risks in government organisations and protect their online services.
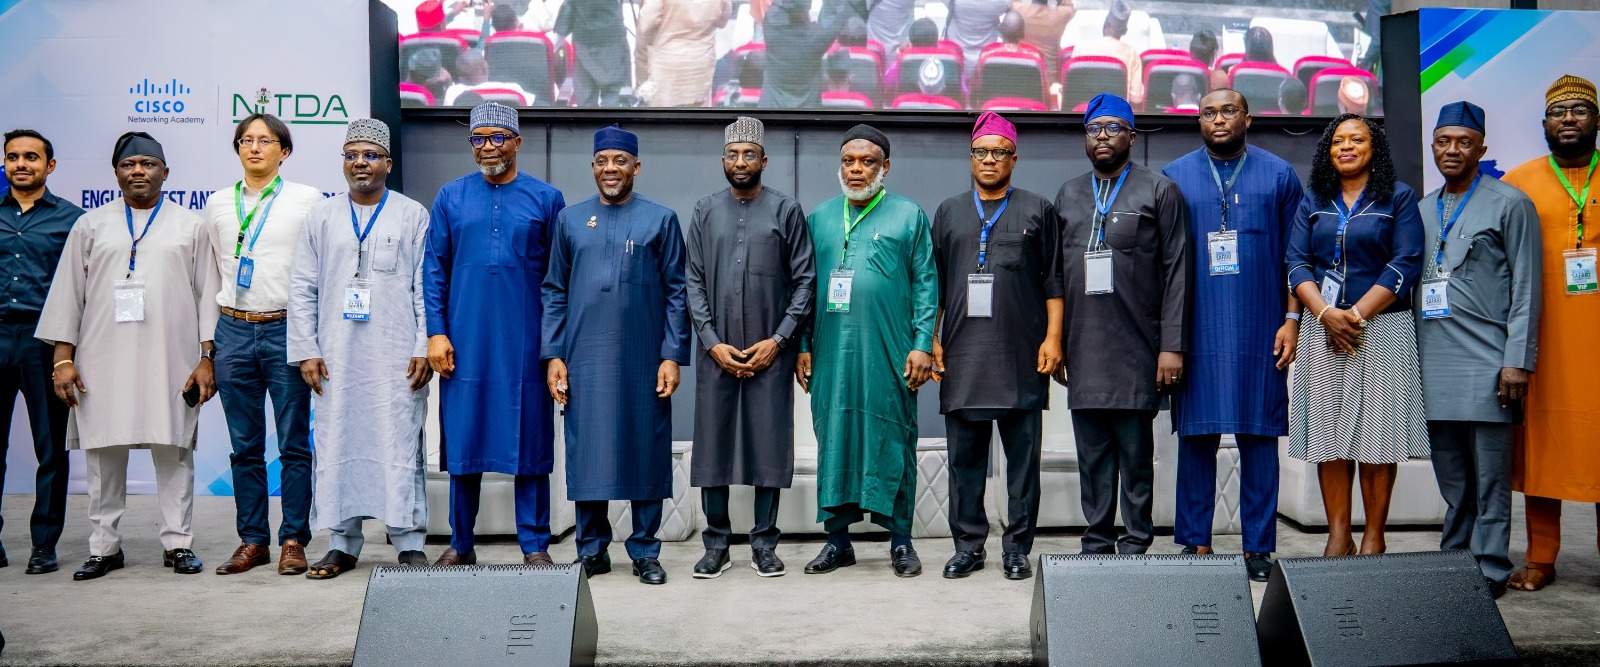
NITDA Director-General, Malam Kashifu Inuwa Abdullahi, stated this at a cybersecurity awareness webinar organised by the Nigeria Internet Registration Association, NiRA, through its .ng Academy. He was represented by Mr Oluwasegun Falayan.
The webinar, held as part of activities for Cybersecurity Awareness Month, was themed, “Securing Nigeria’s Digital Foundation: DNSSEC, the .ng Domain, and the Future of National Cyber Resilience.”
Abdullahi said DNS security should be built into the country’s digital infrastructure to protect domain names and strengthen Nigeria’s presence online.
“DNSSEC is a necessity at the point the country is,” he said, adding that stakeholders must address the challenges to its adoption while NITDA provides an environment for it to thrive.
“Security goes beyond just the physical; our private space must also be secured,” he said.
He said government institutions should take the lead by securing their domains.
“So we must lead. We must ensure that every .gov.ng is signed as much as possible, and we provide DNS as an inclusion in every security assessment that we do,” he said.
“It’s not enough to just have a domain; it must be secured and must be signed.”
NiRA President, Mr Adesola Akinsanya, said organisations should prioritise the quality and security of domain names over the number registered.
He cautioned that poor implementation could disrupt access to websites.
“Where DNSSEC is improperly configured, domains can become inaccessible to users whose resolvers validate signatures,” Akinsanya said. “Our priority must therefore be competence, coordination and careful implementation, rather than adoption for its own sake.”
Explaining the technology, he said the Domain Name System, DNS, functions like the internet’s phonebook, directing users to websites and online services. DNSSEC adds digital signatures that enable validating resolvers to check whether DNS responses are authentic and have been altered.
But he stressed that DNSSEC has limits.
“DNSSEC does not encrypt internet traffic, prevent traffic-flooding attacks, or protect against compromised registrar credentials,” he said. “It is an important layer of security, but it must work alongside other protective measures to create a resilient digital ecosystem.”
Akinsanya cited reports pointing to the scale of cyber threats facing Nigerian organisations and the financial impact of digital fraud.
“Check Point reports that the average Nigerian organisation faced about 4,361 attempted attacks a week in June, against a global average of about 2,270,” he said.
He also cited Nigeria Inter-Bank Settlement System figures showing digital-payment fraud of ₦25.85 billion in 2025, despite a fall in reported incidents.
“NIBSS itself warns that this may signal under-reporting rather than safety,” he said. “DNS security is not a technical hobby. It is an economic question.”
The NiRA president said the Cybersecurity Awareness Month message, “Don’t make it easy for them,” should prompt organisations to address basic security gaps, including unsigned domains and unmonitored changes to domain records.
He said NiRA manages the .ng registry, signs the zone, publishes accurate data and supports registrars, but does not manage individual organisations’ DNS or registrar accounts.
“That is the case for partnership,” he said.
Akinsanya urged government bodies to review who controls their domain accounts and whether multi-factor authentication is enabled. He also called on regulators to include the naming layer in cybersecurity frameworks and critical infrastructure planning, and urged internet providers to enable validation and keep their resolvers updated.
He challenged registrars to improve adoption, saying: “Fifteen of 164 is not a number I can defend.”
Businesses, he added, should ask their service providers whether their domains are signed and who has permission to change their records. Security professionals should share information and report incidents, he said, warning that under-reporting undermines cybersecurity efforts.
Akinsanya said NiRA’s target of growing the .ng namespace by 30 per cent would not come at the expense of security.
“I am not asking for more domains for their own sake. A .ng that is unsafe or unreliable is worse than none,” he said.
He called on registrars, internet service providers, government institutions and technical communities to work together to expand DNSSEC adoption and build implementation capacity.
“Securing our digital foundation is a shared responsibility, and our collective commitment will determine how effectively we protect the future of the .ng namespace and Nigeria’s wider digital economy,” he said.
“A .ng name is more than an address. It is a statement of where you belong and who answers when something goes wrong.”
Speaking during a panel session, the Head of Incident Handling at the Nigeria Computer Emergency Response Team, Daniel Onyekpeze, said cyber incidents were being driven by industrialised social engineering, the use of artificial intelligence and data exposure.
Onyekpeze proposed an Executive Order to give DNSSEC Critical National Information Infrastructure status. He said the technology should be implemented across sectors, including the financial sector, and properly configured.
The Information Technology and Cybersecurity Officer at the Nigeria Data Protection Commission, Abubakar Mahmud, who represented the commission’s National Commissioner and Chief Executive Officer, Dr Vincent Olatunji, said large volumes of data could make organisations targets for attacks.
A representative of the Nigeria Police Force National Cybercrime Centre, SP Kuma Ikyereve, said phishing remained the most common category of cybersecurity cases.
Founder and Chief Executive Officer of CyberPlural, Lateef Hamzat, said attackers were shifting their focus from individuals to systems.
Participants called on organisations to take DNSSEC implementation seriously, arguing that securing digital infrastructure should accompany efforts to expand the number of registered domain names.
They urged organisations to adopt the available DNSSEC resource as part of broader measures to protect their data and online services.